Snyk builds security tools for developers across code, open-source dependencies, containers, and infrastructure as code.
The report
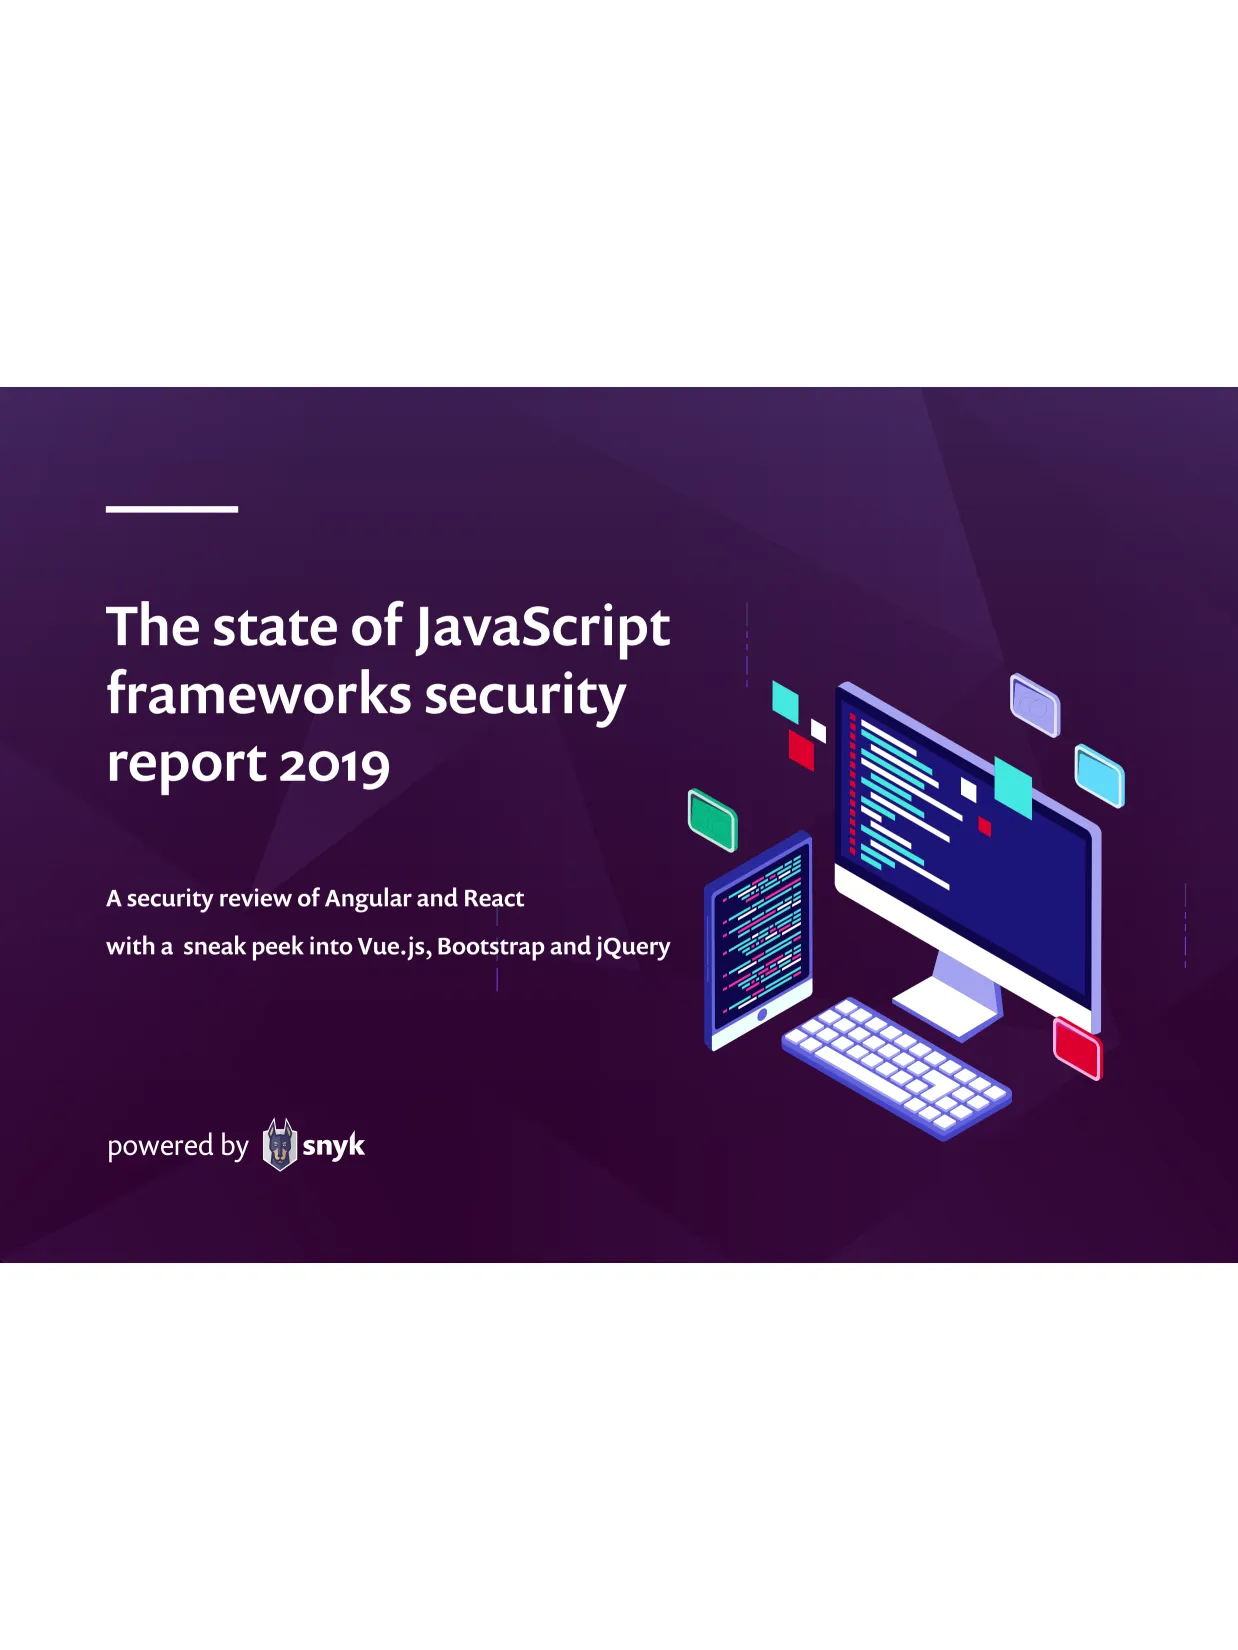
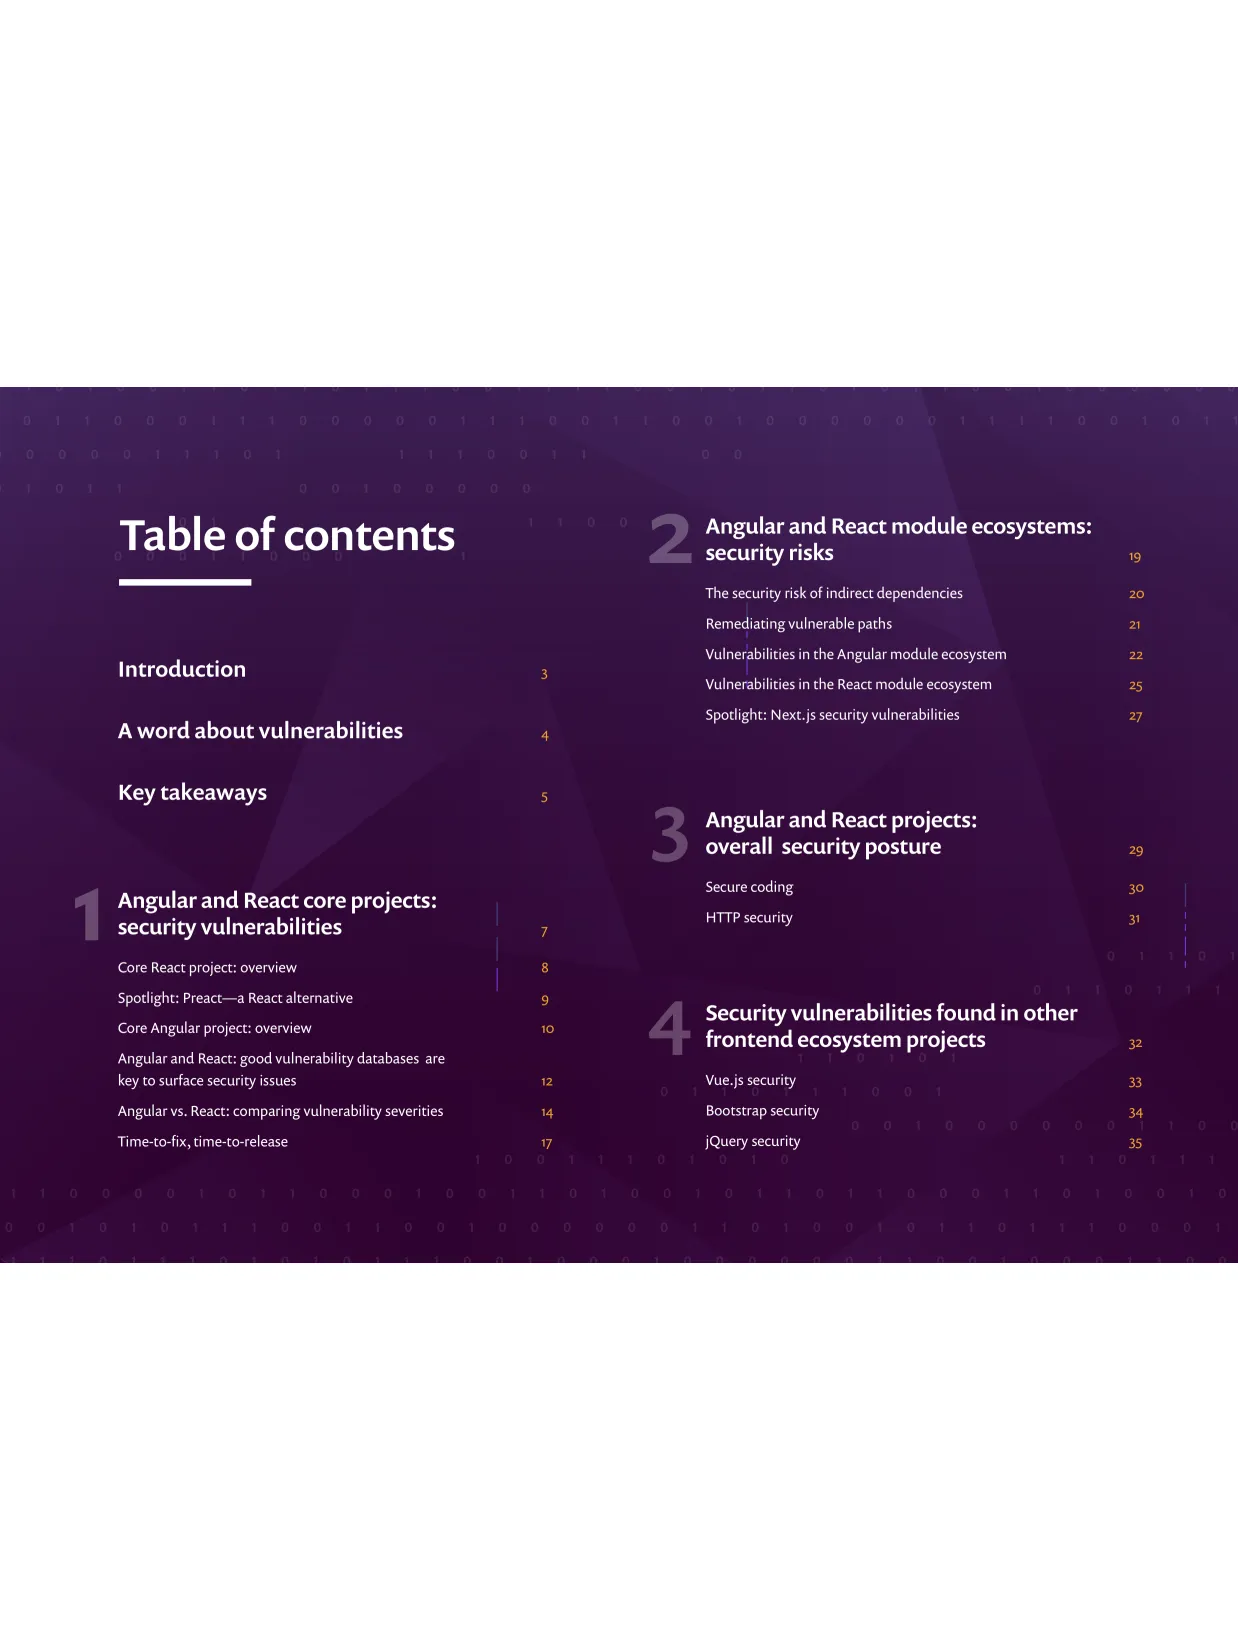
For the report, Snyk's authors examined security risk across the frontend JavaScript frameworks developers were choosing at the time: the risks developers faced in each framework, what teams inherited through dependencies, and what developers could do about both. Keeping the voice, technical depth, and terms consistent across that material was part of my job.
My role
As ghost editor, I kept one voice and one level of technical detail across the full piece, checked claims against the research, and kept the remediation guidance specific enough for a developer to use.
The wider engagement
I also worked with Snyk across content, documentation, and technical resources, including the PCI DSS article, the post on prioritizing exploits seen in the wild, and technical and marketing video.
Why it mattered
At Snyk, I was the founding documentation individual contributor. Snyk's team was teaching developers to treat application security as part of their own work, and we had to explain the technical problem in terms developers could act on.