Snyk is security tooling for developers, covering code, dependencies, containers and infrastructure as code, having been at the forefront of the shift-left movement. To "shift left" means integrating tasks and processes such as software testing, reliability, and operational practices into the early stages of development, sharing responsibility with engineers as well as the more traditional roles: QA, reliability teams, and so on.
The challenge: new regulations shifted left too
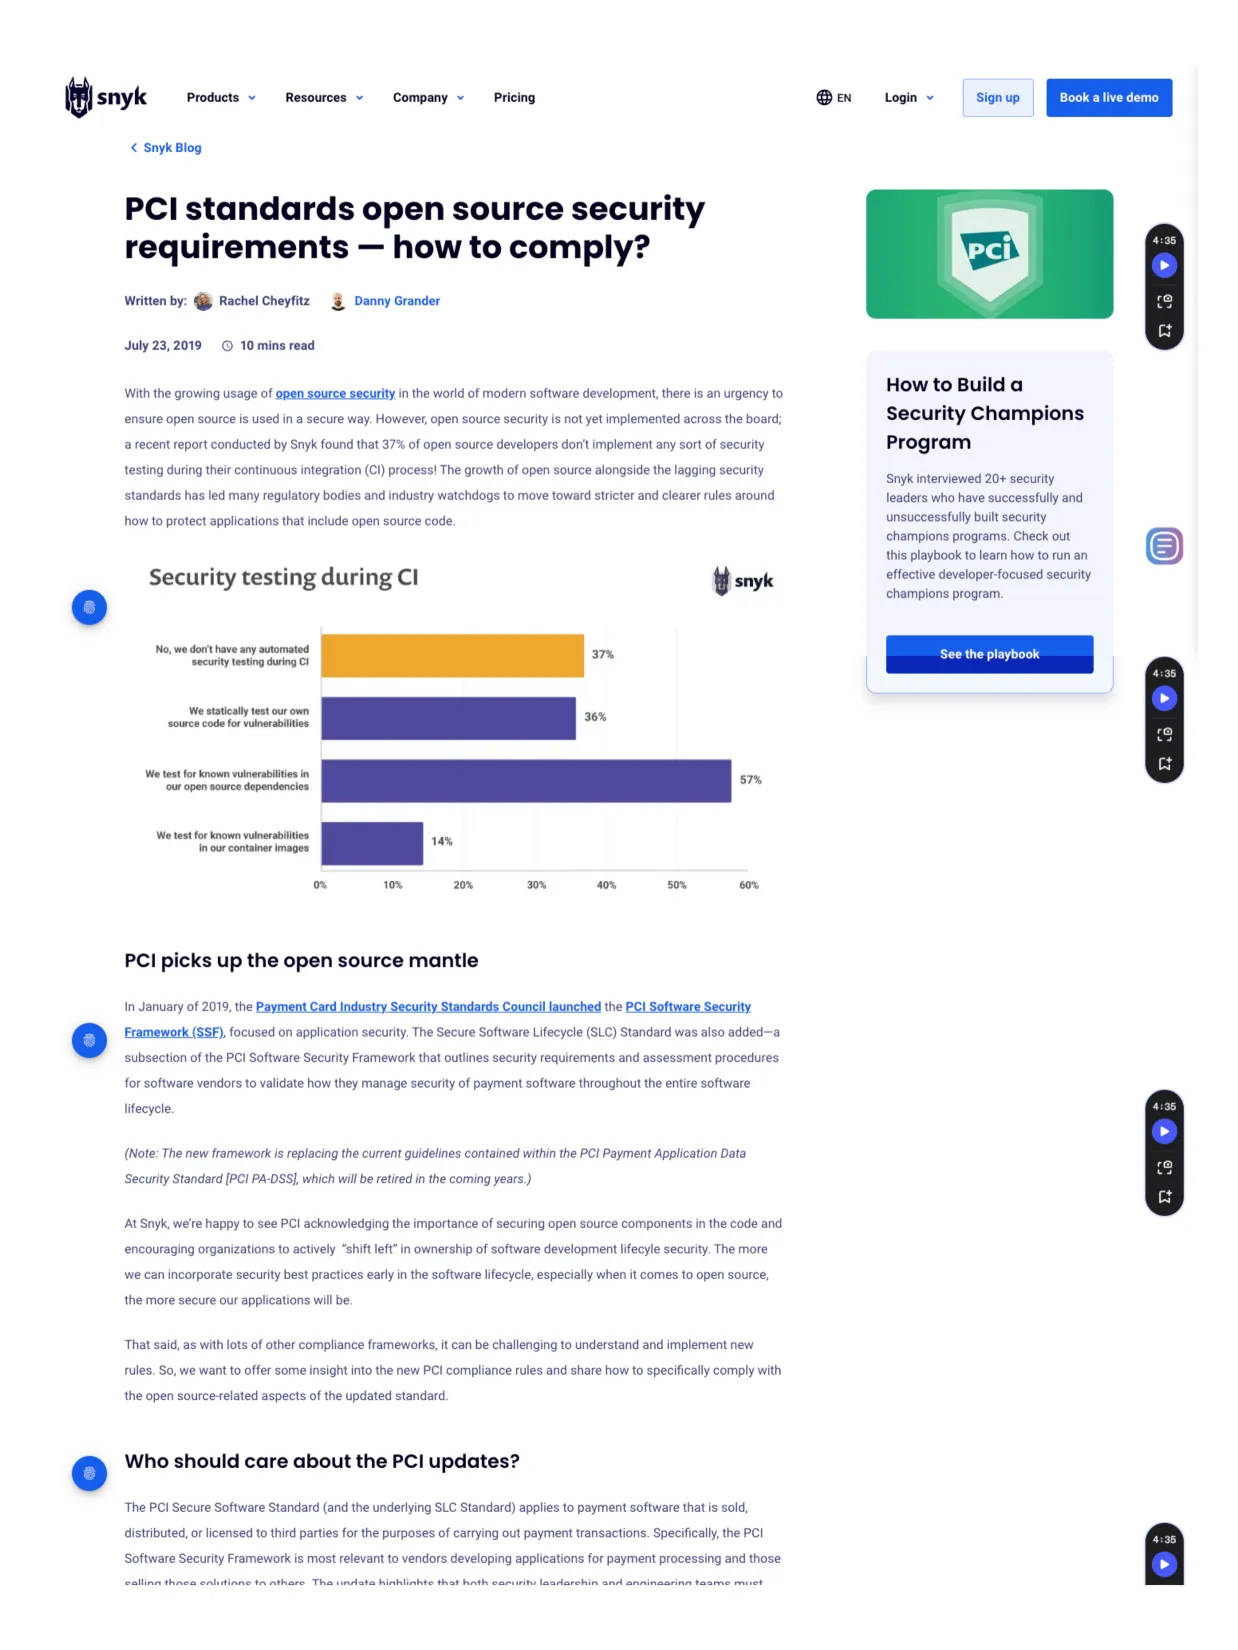
In January of 2019, the Payment Card Industry Security Standards Council launched the PCI Software Security Framework (SSE), focused on application security. The Secure Software Lifecycle (SLC) Standard was also added as a subsection of the PCI Software Security Framework that outlines security requirements and assessment procedures for software vendors to validate how they manage security of payment software throughout the entire software lifecycle.
The solution: market education and product launches
I wrote it with Danny Grander, Snyk’s co-founder and CTO, including what the standard requires, and what open-source dependencies cost a real codebase.
Not longer after we released this post, we released supporting features in the product, about which we wrote separately.
Why
As a leader in the shift-left movement, this was important information that developers taking on these new responsibilities needed to understand more of. This was a new opportunity for Snyk in market educatoin, and also for product development.