Alcide was a Tel Aviv company building security for Kubernetes clusters.
The context
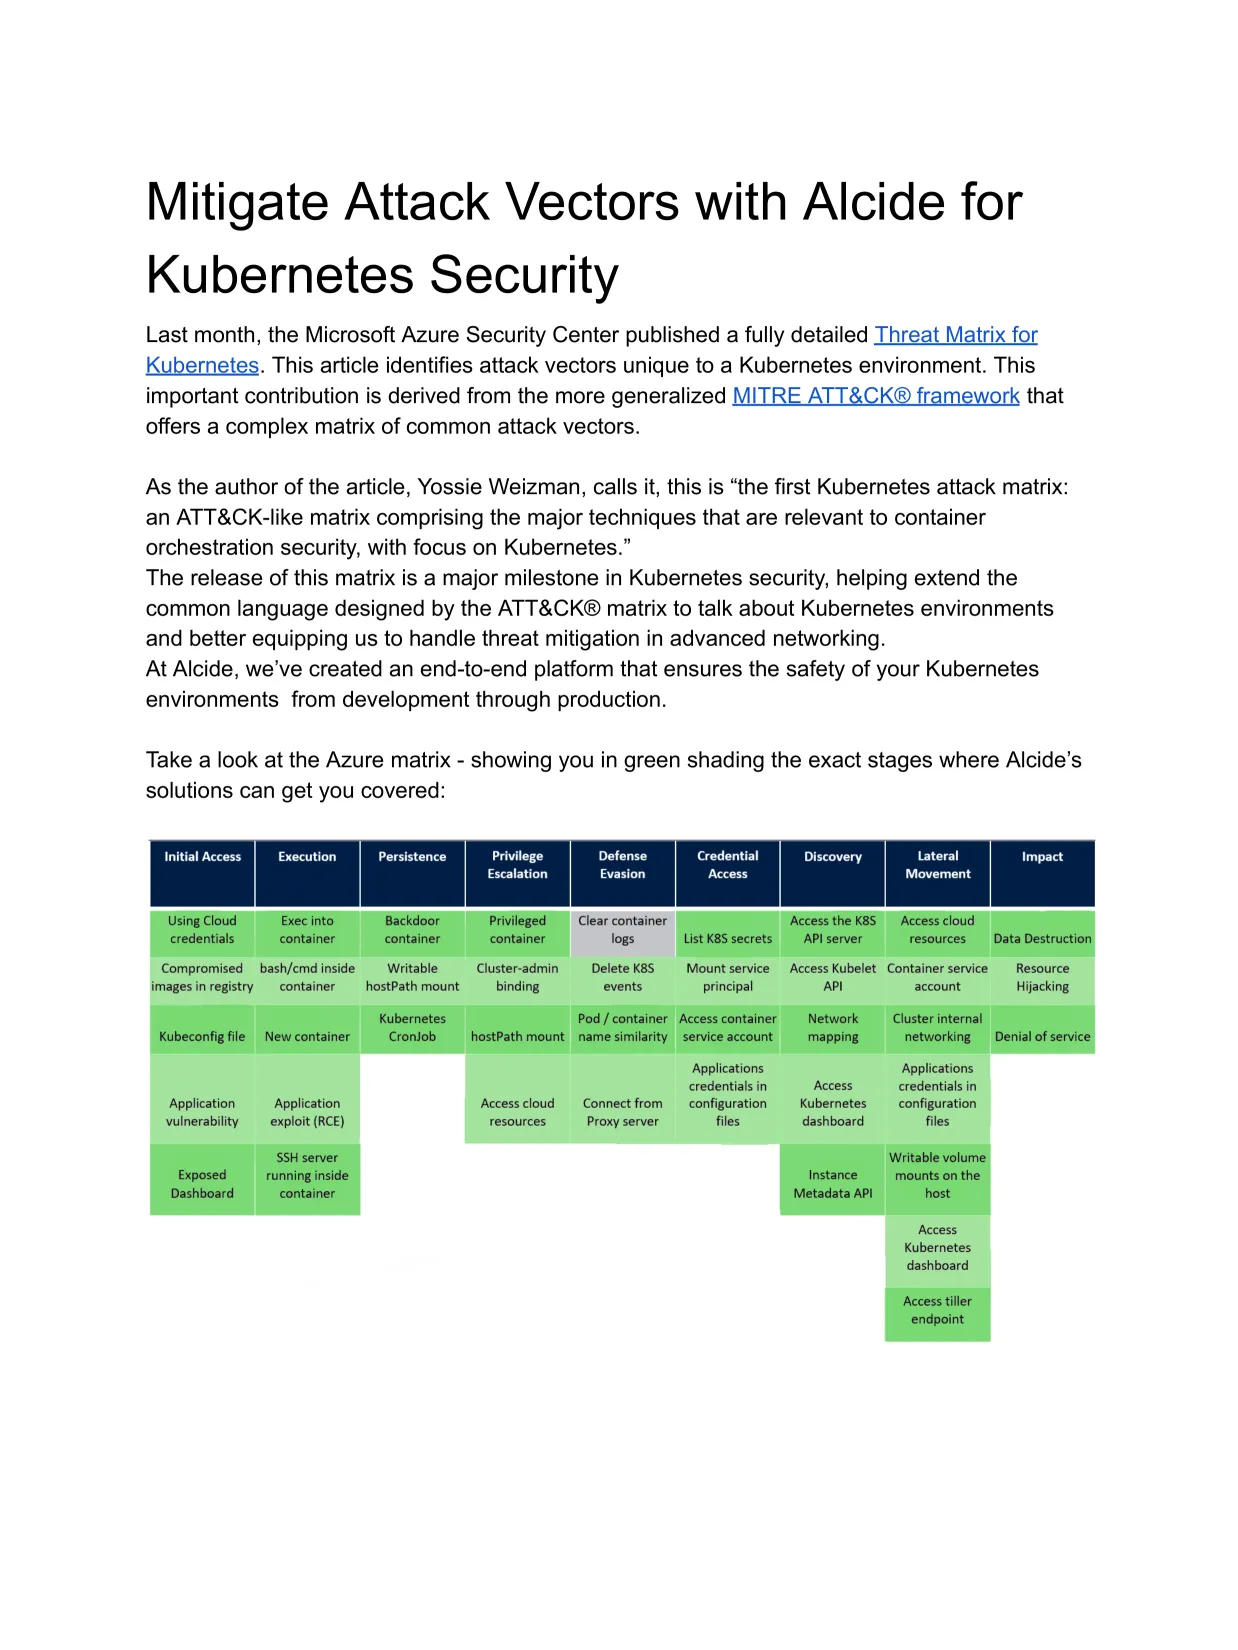
In 2020, Microsoft's Azure Security Center published a preliminary ATT&CK-style threat matrix for Kubernetes. Security teams already used ATT&CK tactics and techniques in other parts of their work, while Kubernetes still lacked an established equivalent from MITRE. Vendors could all claim Kubernetes security, and buyers had no common way to compare coverage inside a cluster.
The paper
Alcide's founding team initiated and led the work using its own product knowledge and excluding customer information. As technical editor, I built the structure with the authors, pushed for the level of detail a security reader would expect, and kept the mapping precise wherever the product covered only part of a technique.
Why ATT&CK
I used the ATT&CK vocabulary because security teams already knew it. Using that vocabulary, I mapped the product to the same tactics and techniques so readers could inspect what Alcide covered and where the coverage was partial.